
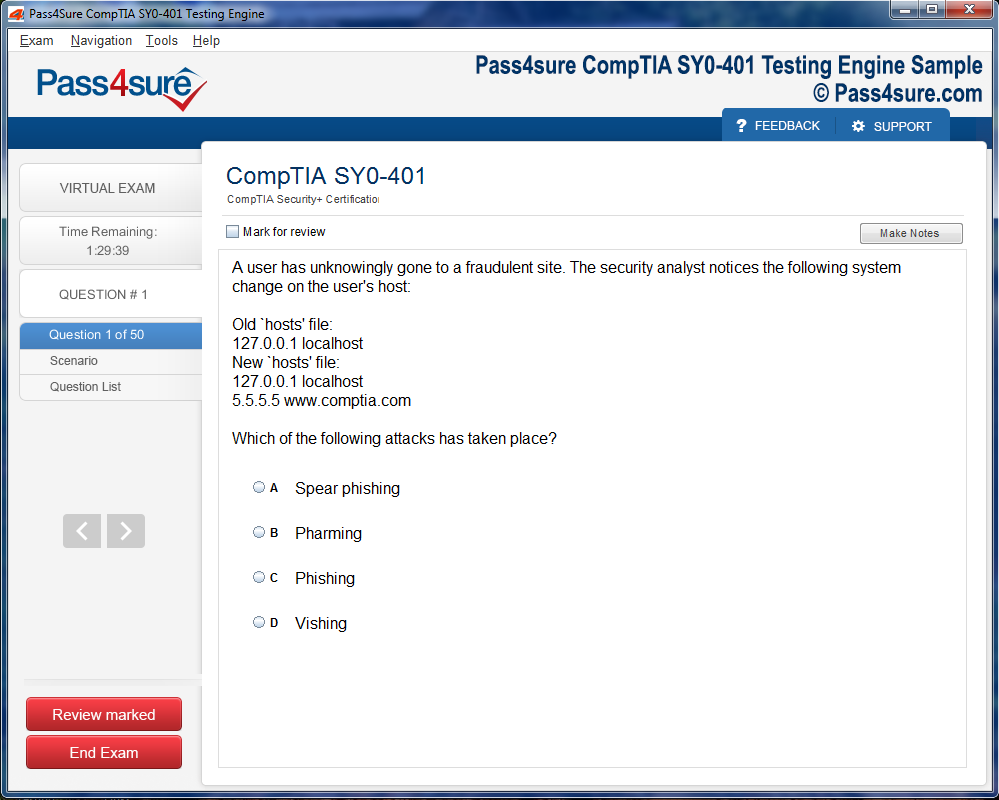
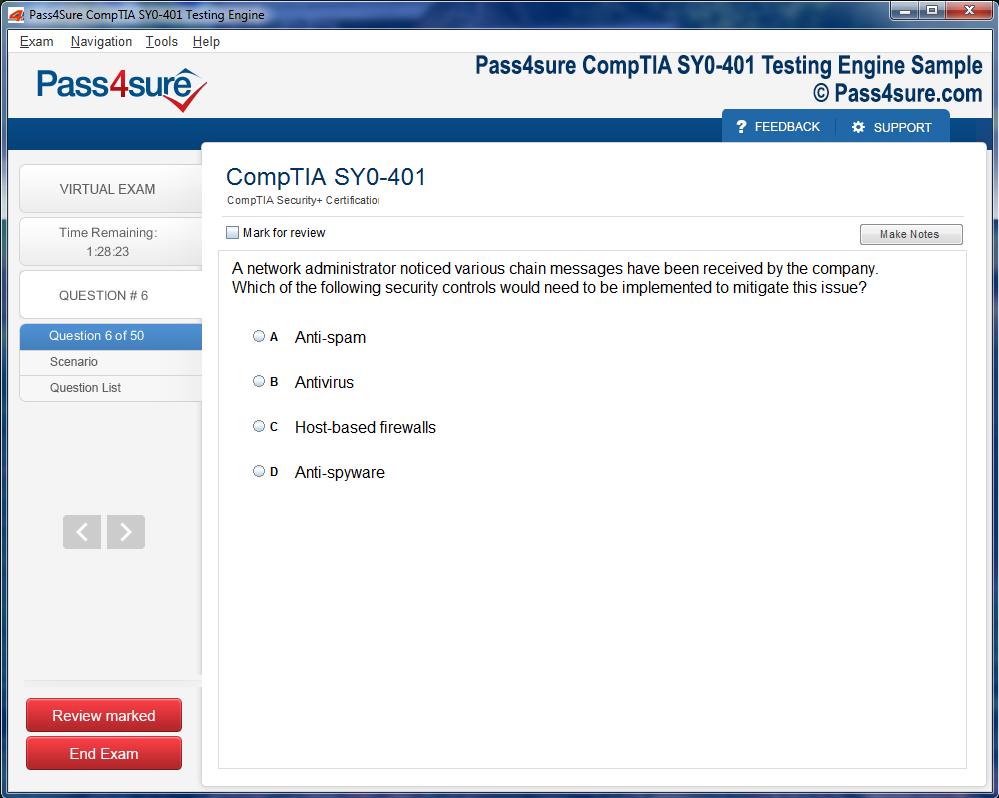
Product Screenshots
Frequently Asked Questions
How does your testing engine works?
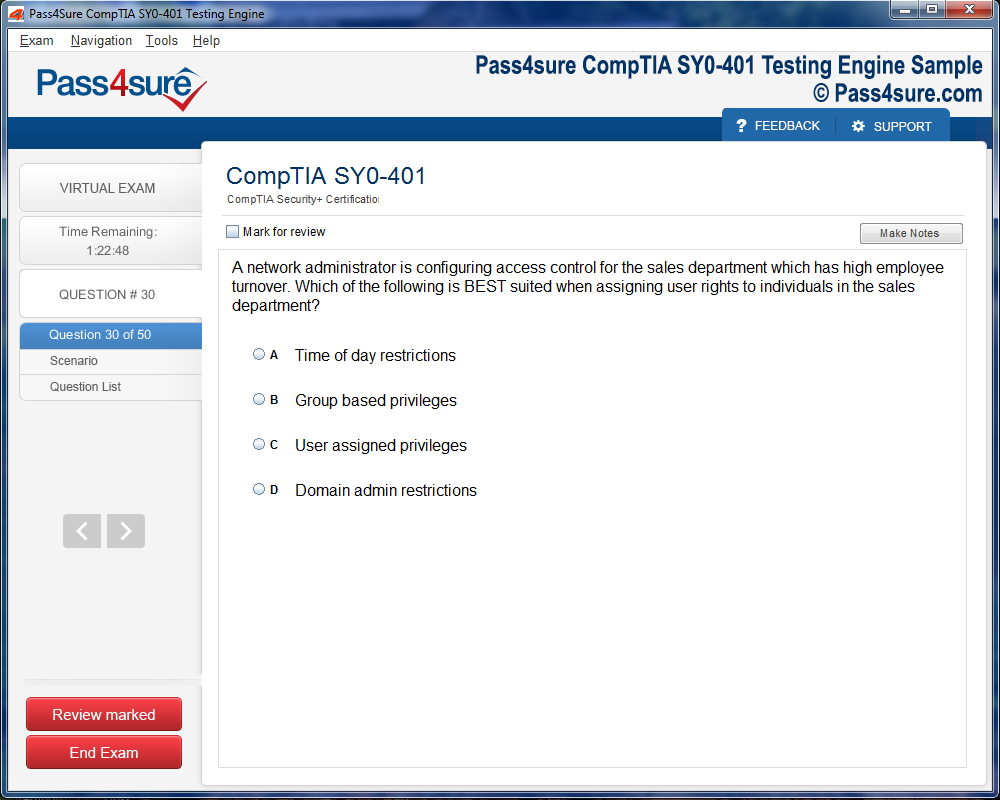
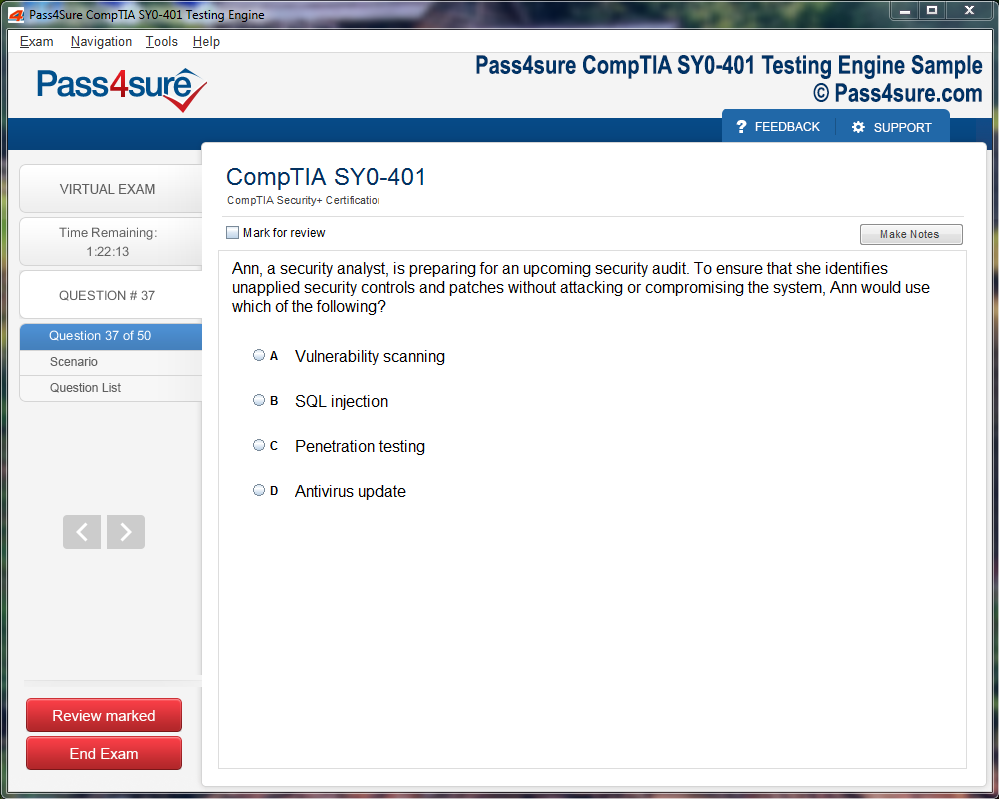
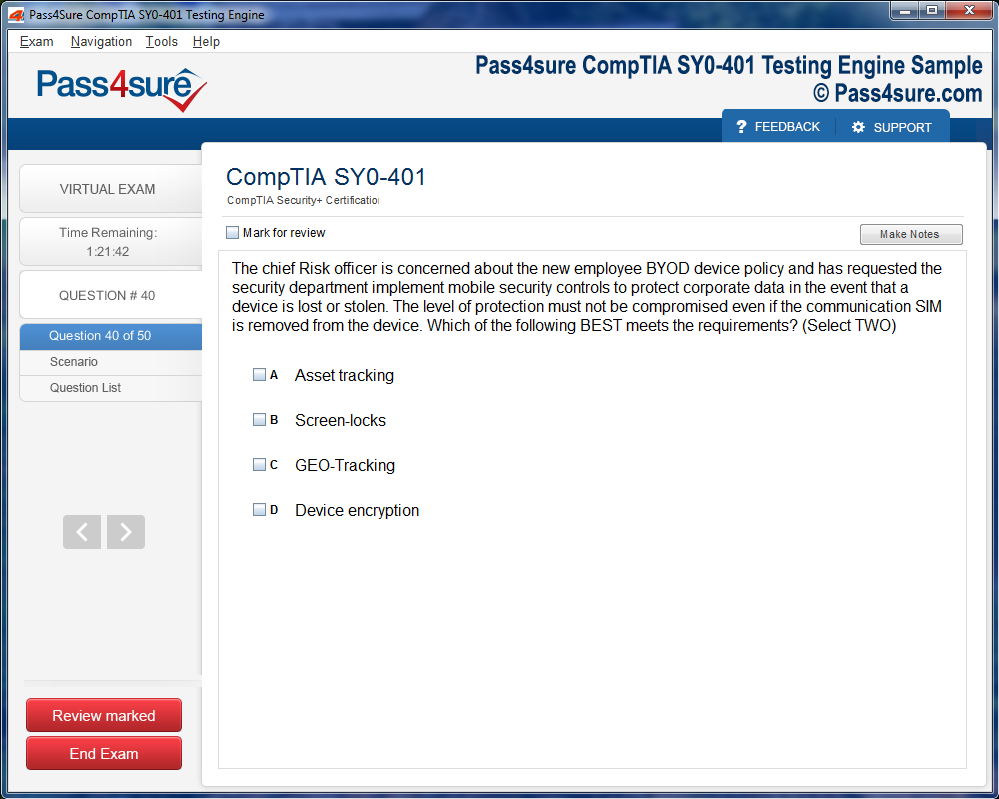
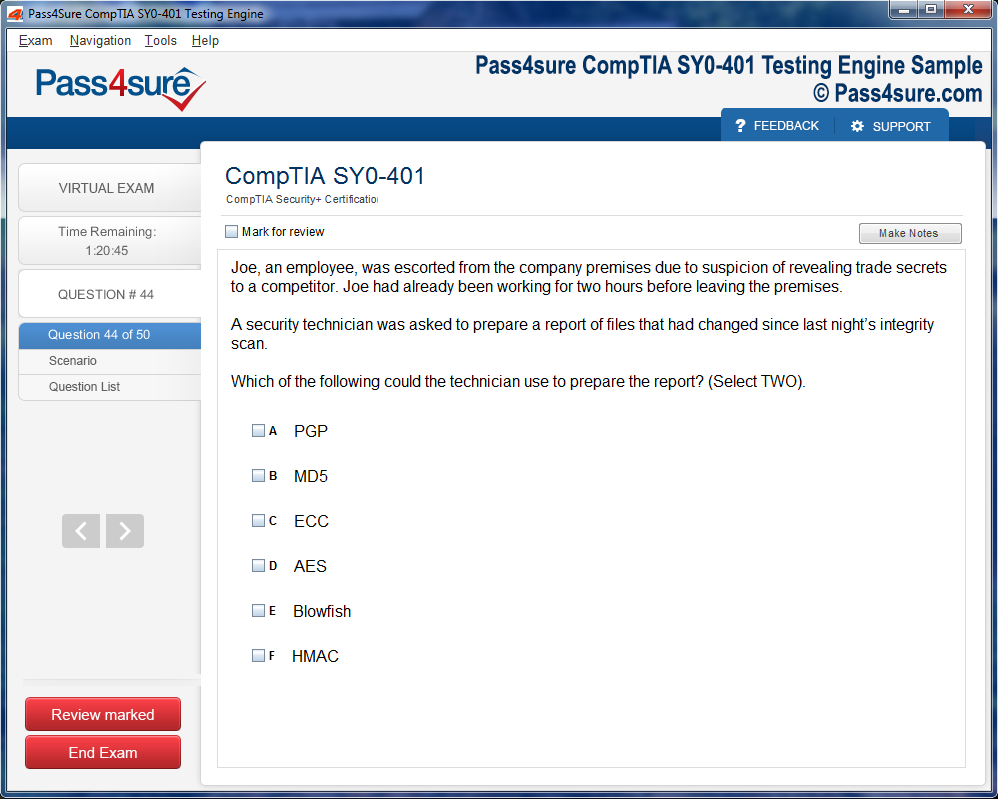
Once download and installed on your PC, you can practise test questions, review your questions & answers using two different options 'practice exam' and 'virtual exam'. Virtual Exam - test yourself with exam questions with a time limit, as if you are taking exams in the Prometric or VUE testing centre. Practice exam - review exam questions one by one, see correct answers and explanations.
How can I get the products after purchase?
All products are available for download immediately from your Member's Area. Once you have made the payment, you will be transferred to Member's Area where you can login and download the products you have purchased to your computer.
How long can I use my product? Will it be valid forever?
Pass4sure products have a validity of 90 days from the date of purchase. This means that any updates to the products, including but not limited to new questions, or updates and changes by our editing team, will be automatically downloaded on to computer to make sure that you get latest exam prep materials during those 90 days.
Can I renew my product if when it's expired?
Yes, when the 90 days of your product validity are over, you have the option of renewing your expired products with a 30% discount. This can be done in your Member's Area.
Please note that you will not be able to use the product after it has expired if you don't renew it.
How often are the questions updated?
We always try to provide the latest pool of questions, Updates in the questions depend on the changes in actual pool of questions by different vendors. As soon as we know about the change in the exam question pool we try our best to update the products as fast as possible.
How many computers I can download Pass4sure software on?
You can download the Pass4sure products on the maximum number of 2 (two) computers or devices. If you need to use the software on more than two machines, you can purchase this option separately. Please email sales@pass4sure.com if you need to use more than 5 (five) computers.
What are the system requirements?
Minimum System Requirements:
- Windows XP or newer operating system
- Java Version 8 or newer
- 1+ GHz processor
- 1 GB Ram
- 50 MB available hard disk typically (products may vary)
What operating systems are supported by your Testing Engine software?
Our testing engine is supported by Windows. Andriod and IOS software is currently under development.
EC-Council 212-82 Certification: A Clear Path to Cybersecurity Success
The EC-Council 212-82 exam is the qualifying assessment for the Certified Cybersecurity Technician credential, which EC-Council designed as a foundational entry point into the professional cybersecurity certification landscape. EC-Council, which stands for the International Council of Electronic Commerce Consultants, is one of the most recognized certification bodies in the information security industry, known globally for credentials including the Certified Ethical Hacker and the Certified Network Defender. The Certified Cybersecurity Technician represents EC-Council's response to a growing industry need for a rigorous but accessible credential that validates practical cybersecurity competency at the technician level, serving professionals who are beginning their cybersecurity careers or transitioning into security roles from adjacent technology disciplines.
The cybersecurity industry faces a well-documented and persistent talent shortage that shows no signs of resolving itself in the near term. Organizations across every sector struggle to find qualified professionals who can protect their digital assets, respond to security incidents, and maintain the operational security posture that modern threat environments demand. The Certified Cybersecurity Technician credential addresses this shortage by providing a structured and vendor-neutral pathway for aspiring cybersecurity professionals to validate their foundational knowledge and practical skills through a rigorous assessment that covers the full breadth of core cybersecurity disciplines. For candidates who want to enter the cybersecurity field with a credential that carries genuine industry recognition and validates real practical competency rather than just theoretical awareness, the 212-82 exam represents a compelling and worthwhile pursuit.
What the Certified Cybersecurity Technician Credential Represents
The Certified Cybersecurity Technician is deliberately positioned as a technician-level credential rather than an analyst or professional-level certification, and this positioning reflects a specific and intentional design philosophy. EC-Council built the credential to validate the hands-on technical skills that cybersecurity technicians apply in day-to-day operational security work, including network defense, threat detection, vulnerability assessment, incident response, and security operations tasks that form the foundation of organizational security programs. The credential does not presuppose years of deep security experience, but it does expect candidates to engage with practical scenarios and demonstrate that they can apply security knowledge in realistic operational contexts.
EC-Council structured the Certified Cybersecurity Technician program around a combination of conceptual knowledge and hands-on laboratory exercises that expose candidates to real security tools and techniques in a controlled training environment. This practical orientation distinguishes the credential from purely knowledge-based certifications and aligns it more closely with the actual work that security technicians perform. Employers who see the Certified Cybersecurity Technician on a candidate's resume can reasonably infer that the holder has not only studied cybersecurity concepts but has also worked through practical exercises that simulate real operational security scenarios, making the credential a more meaningful hiring signal than certifications that assess only theoretical knowledge.
Exam Format and Assessment Structure
The 212-82 exam consists of 125 multiple-choice questions that must be completed within a four-hour time window, which is notably generous compared to many other professional certification exams and reflects the technical depth and scenario complexity of the questions candidates will encounter. The passing score for the exam is set at 70 percent, meaning candidates must answer at least 88 of the 125 questions correctly to earn the credential. The exam is delivered through EC-Council's testing infrastructure and is available through authorized testing centers as well as through online proctored delivery for candidates who meet the technical requirements for remote examination.
The question style in the 212-82 exam leans heavily toward scenario-based assessment, presenting candidates with realistic descriptions of security situations and asking them to identify the correct technical response, the appropriate tool or technique, or the most accurate interpretation of presented information. This scenario orientation means that candidates who have developed genuine understanding of cybersecurity concepts and their practical application will consistently outperform those who have attempted to prepare through memorization alone. The four-hour time allocation gives candidates enough time to read each scenario carefully, reason through the answer options methodically, and revisit flagged questions before submitting their final responses, making time management a less critical concern than it is in exams with tighter constraints.
The Nine Core Knowledge Domains
EC-Council organizes the 212-82 exam content around nine primary knowledge domains that together span the breadth of foundational cybersecurity practice. These domains are information security threats and vulnerabilities, information security attacks, network security fundamentals, identification and authentication and authorization, network security controls and protocols, administrative security, cryptography, data security, and network troubleshooting. Each domain addresses a distinct dimension of cybersecurity knowledge and practice, and the exam draws questions from all nine domains in proportions that reflect their relative importance to the work of a cybersecurity technician.
Understanding the scope and content of each domain before beginning preparation allows candidates to develop a study plan that allocates time proportionally to coverage weight and personal knowledge gaps. Candidates who take a diagnostic practice assessment early in their preparation process can identify which domains require the most intensive study and which areas they can address more efficiently because of existing background knowledge. This targeted approach to preparation produces better outcomes than treating all nine domains as equally unfamiliar territory and spending equal time on each regardless of starting competency level.
Information Security Threats and Attack Landscape
The threat and vulnerability domain establishes the conceptual foundation for everything else in the exam by ensuring that candidates understand the nature of the adversarial landscape that cybersecurity professionals work within. This domain covers the classification of threats by their origin, motivation, and technical sophistication, including the distinction between internal and external threats, opportunistic and targeted attacks, and the range of threat actor categories from script kiddies and hacktivists through organized criminal groups and nation-state sponsored advanced persistent threat actors. Understanding who attacks organizations and why they do so provides essential context for evaluating the relevance and priority of different security controls.
Vulnerability concepts are central to this domain, including the difference between a vulnerability, a threat, and a risk and how these three concepts relate to one another within the broader framework of information security risk management. Common vulnerability categories including software flaws, configuration weaknesses, unpatched systems, insecure default settings, and human factors are all covered at a level of depth that prepares candidates to recognize vulnerability conditions in described scenarios. The Common Vulnerability Scoring System, which provides a standardized framework for assessing and communicating the severity of identified vulnerabilities, is an important topic that candidates should understand both conceptually and in terms of how its scores are interpreted and used to prioritize remediation efforts.
Network Security Fundamentals and Protocol Knowledge
Network security is one of the most technically substantive domains in the 212-82 exam, requiring candidates to have a solid understanding of how networks are constructed, how data flows through them, and where security controls can be applied to protect that data in transit and at rest. The domain builds on foundational networking concepts including the OSI and TCP/IP reference models, IP addressing and subnetting, routing and switching fundamentals, and the behavior of core protocols including DNS, DHCP, HTTP, HTTPS, FTP, SMTP, and SSH. Candidates who have a strong networking background will find this domain more accessible than those approaching it without prior networking knowledge, and those in the latter group should plan to invest additional preparation time in building their networking fundamentals before tackling the security-specific content.
Firewall technology is a central topic within this domain, covering the different types of firewalls including packet filtering, stateful inspection, application layer, and next-generation firewalls, their respective capabilities and limitations, and the principles that guide effective firewall rule design. Intrusion detection and intrusion prevention systems are closely related topics that the exam covers in meaningful depth, including the difference between signature-based and anomaly-based detection approaches, the distinction between detection and prevention modes of operation, and the placement considerations that affect how effectively these systems can monitor network traffic. Virtual private network technology, including both site-to-site and remote access VPN configurations, is another important network security topic that candidates should understand at both a conceptual and a practical level.
Identification, Authentication, and Access Control
The identity and access management domain covers the principles and mechanisms through which organizations verify the identities of users and systems and control what resources those verified identities are permitted to access. Authentication is the process of verifying that a claimed identity is genuine, and the exam covers the three primary authentication factors including something a user knows such as a password, something a user has such as a hardware token or smart card, and something a user is such as a biometric characteristic. Multi-factor authentication, which combines two or more of these factors to provide stronger assurance than any single factor can deliver alone, is a topic that receives significant exam attention because of its central importance to modern identity security.
Access control models define the rules and mechanisms through which systems enforce authorization decisions after authentication is complete. The exam covers the major access control models including discretionary access control where resource owners control access permissions, mandatory access control where system-enforced policies based on security labels govern access, role-based access control where permissions are assigned to roles rather than individuals, and attribute-based access control where access decisions are made based on a combination of user, resource, and environmental attributes. The principle of least privilege, which states that users and systems should be granted only the minimum access necessary to perform their legitimate functions, is a foundational security concept that candidates should understand deeply because it underlies effective access control design across all of these models.
Cryptography Concepts and Practical Applications
Cryptography is one of the most conceptually demanding domains in the 212-82 exam, requiring candidates to understand the mathematical and logical principles that underpin modern encryption and related security technologies well enough to apply that understanding in practical security scenarios. The exam covers the fundamental distinction between symmetric and asymmetric encryption, including how each approach works at a conceptual level, the trade-offs between them in terms of performance and key management complexity, and the contexts in which each is most appropriately used. Common symmetric algorithms including AES and 3DES and asymmetric algorithms including RSA and elliptic curve cryptography are covered, along with the key lengths and security properties associated with each.
Hashing algorithms and their role in data integrity verification and password storage are important cryptography topics that the exam addresses in meaningful depth. Candidates should understand how cryptographic hash functions differ from encryption, why they are one-way functions that cannot be reversed, and how they are used to create digital signatures and message authentication codes that verify both the integrity and the authenticity of data. Public key infrastructure concepts including certificate authorities, digital certificates, certificate revocation, and the chain of trust that allows relying parties to verify certificate validity are essential knowledge for candidates, as PKI underpins the security of HTTPS, secure email, code signing, and many other critical security technologies. The exam also covers common cryptographic attacks including brute force, dictionary attacks, rainbow table attacks, and birthday attacks, along with the defenses such as salting that protect against them.
Security Operations and Incident Response
Security operations is a domain that reflects the day-to-day operational work of cybersecurity technicians who monitor organizational environments for signs of malicious activity, investigate alerts and anomalies, and respond to confirmed security incidents in ways that contain damage and restore normal operations as quickly as possible. The exam covers security operations center concepts including the roles and responsibilities of security analysts, the tools used for security monitoring and analysis, and the processes through which alerts are triaged, investigated, and escalated. Security information and event management platforms, which aggregate and correlate log data from across the organization to identify patterns indicative of security threats, are an important operational security technology that candidates should understand at a functional level.
Incident response is a structured process for managing security incidents from initial detection through containment, eradication, recovery, and post-incident analysis, and the exam tests candidates on the phases of this process and the key activities associated with each phase. The ability to classify incidents by type and severity, apply appropriate containment strategies based on incident characteristics, preserve forensic evidence correctly to support subsequent investigation and potential legal proceedings, and conduct a meaningful post-incident review that produces actionable lessons for improving future response capabilities are all competencies that the exam assesses through scenario-based questions. Digital forensics concepts including evidence collection, chain of custody, forensic imaging, and the use of forensic analysis tools are related topics that receive coverage within this domain.
Vulnerability Assessment and Security Testing
The vulnerability assessment domain covers the systematic processes and tools used to identify security weaknesses in organizational systems, networks, and applications before attackers can exploit them. Candidates need to understand the difference between vulnerability scanning, which uses automated tools to identify known vulnerabilities in systems based on their versions, configurations, and exposed services, and penetration testing, which goes further by attempting to actively exploit identified vulnerabilities to demonstrate their real-world impact. The exam also covers the distinction between black box testing where the tester has no prior knowledge of the target environment, white box testing where full system information is provided, and grey box testing which falls between these two extremes.
Common vulnerability scanning tools including Nessus, OpenVAS, and Qualys are topics that candidates should be familiar with at a functional level, understanding what these tools do, how they are deployed, and how their output is interpreted and acted upon. The concept of a vulnerability management program, which goes beyond individual scan events to establish a continuous cycle of discovery, assessment, prioritization, remediation, and verification, is important organizational security knowledge that the exam covers. Patch management processes, which represent the primary remediation mechanism for many categories of vulnerability, are closely related and the exam tests candidates on the principles and challenges of effective patch management in complex enterprise environments.
Data Security and Privacy Protection
Data security is a domain that addresses one of the most fundamental responsibilities of any cybersecurity program, which is protecting the confidentiality, integrity, and availability of organizational data assets throughout their entire lifecycle from creation through storage, transmission, use, and eventual disposal. The exam covers data classification frameworks that help organizations identify which data requires the strongest protection based on its sensitivity and the potential impact of its unauthorized disclosure or modification. Common classification tiers including public, internal, confidential, and restricted data categories reflect the kind of practical classification systems that organizations implement to guide their data protection investments and controls.
Data loss prevention technology, which provides the technical mechanisms for detecting and preventing the unauthorized transmission or copying of sensitive data, is an important data security topic that candidates should understand at a functional level. Encryption of data at rest and data in transit is covered as a primary technical control for protecting data confidentiality, and candidates should understand which scenarios call for each approach and which encryption technologies are appropriate for different data types and transmission channels. Privacy regulations including the General Data Protection Regulation and various national and sector-specific privacy frameworks are covered at a conceptual level sufficient for candidates to understand the regulatory context within which organizational data security programs operate and the consequences of failing to protect personal data adequately.
Administrative Security and Governance Concepts
Administrative security covers the policies, procedures, frameworks, and organizational structures through which cybersecurity programs are governed, managed, and continuously improved. This domain reflects the reality that technical security controls alone are insufficient to protect organizations effectively without the supporting infrastructure of well-designed policies that define security expectations, procedures that specify how security tasks are performed correctly, training programs that build security awareness across the workforce, and governance frameworks that ensure accountability for security outcomes at appropriate organizational levels.
Security policies are the foundational administrative controls that define an organization's security requirements and expectations, and the exam covers the different types of policies including acceptable use policies, password policies, data classification policies, and incident response policies that together constitute a comprehensive policy framework. Security awareness training programs are an essential administrative control for addressing the human factor in organizational security, and candidates should understand the key elements of effective security awareness programs and how they reduce the likelihood of social engineering attacks and security policy violations. Risk management frameworks including those published by the National Institute of Standards and Technology provide structured approaches to identifying, assessing, and managing cybersecurity risks, and familiarity with these frameworks at a conceptual level is useful preparation for the administrative security domain questions in the exam.
Study Resources and Hands-On Preparation
EC-Council provides official training materials for the Certified Cybersecurity Technician program through its authorized training centers and through the iLearn self-paced learning platform, which offers video instruction, electronic courseware, and access to the practical laboratory environment that is integral to the program. The official EC-Council courseware is the most closely aligned study material available for the 212-82 exam and should be the primary preparation resource for candidates who want to ensure their study content matches the exam's scope and emphasis as accurately as possible.
The practical laboratory component of the EC-Council Certified Cybersecurity Technician program is one of its most valuable preparation elements, providing candidates with hands-on experience using real security tools in simulated scenarios that mirror the kinds of situations they will encounter both in the exam and in actual cybersecurity work. Candidates who complete the lab exercises thoroughly and engage with them seriously rather than simply clicking through to record completion develop a practical fluency with security tools and techniques that significantly improves their performance on the scenario-based exam questions. Supplementary resources including practice exams from reputable third-party providers, security-focused video training from platforms like Cybrary, and community resources from security practitioner forums and study groups can complement the official materials and provide additional perspective on challenging topics.
Conclusion
The EC-Council 212-82 exam and the Certified Cybersecurity Technician credential it awards represent a genuinely valuable entry point into the professional cybersecurity certification landscape for candidates who approach their preparation with seriousness, intellectual engagement, and a commitment to developing real practical competency rather than simply accumulating a credential. The cybersecurity field is one where the gap between certified knowledge and operational capability matters enormously, because security failures have real consequences for organizations and the people who depend on them. The Certified Cybersecurity Technician program's emphasis on practical laboratory exercises alongside conceptual knowledge assessment reflects an understanding of this reality and produces graduates who are meaningfully better prepared for the demands of entry-level cybersecurity roles than candidates who hold purely knowledge-based credentials.
The nine domains covered by the 212-82 exam span a genuinely broad range of cybersecurity knowledge and practice, from the conceptual foundations of threat and vulnerability understanding through the technical depth of cryptography and network security to the operational realities of incident response and security operations center work. Candidates who work through all nine domains systematically and honestly, investing extra effort in the areas where their existing knowledge is weakest, emerge from the preparation process with a significantly more complete picture of the cybersecurity discipline than they had when they began. This comprehensive foundation is valuable not just for passing the exam but for navigating the early stages of a cybersecurity career with confidence and competence.
The cybersecurity profession rewards continuous learning in ways that few other technical disciplines match, because the threat landscape evolves constantly and the tools, techniques, and knowledge that were current yesterday may be insufficient against the attacks of tomorrow. Professionals who earn the Certified Cybersecurity Technician credential and then rest on it without continuing to develop their knowledge and skills will find that the advantage it confers diminishes over time. The most successful cybersecurity careers belong to those who treat the credential as a beginning rather than a destination, using it as a foundation upon which to build progressively deeper and more specialized expertise through additional certifications, hands-on practice, continued education, and active participation in the security community.
For candidates who are making their first serious investment in cybersecurity professional development, the Certified Cybersecurity Technician represents a rigorous and respected credential that provides real value in the job market and genuine preparation for the work of protecting organizations against an increasingly sophisticated and persistent threat landscape. The preparation journey demands genuine effort and intellectual engagement, but it repays that effort with knowledge and practical skills that serve certified professionals throughout careers devoted to one of the most important and meaningful disciplines in modern technology. Every hour invested in thorough preparation for the 212-82 exam is an investment in the capability to protect the systems, data, and people that organizations depend upon, and that is an investment whose returns extend far beyond the certification itself.
Top ECCouncil Exams
- 312-50v13 - Certified Ethical Hacker v13
- 212-89 - EC-Council Certified Incident Handler
- 712-50 - EC-Council Certified CISO
- 312-85 - Certified Threat Intelligence Analyst
- 312-39v2 - Certified SOC Analyst (CSA) v2
- 312-49v11 - Computer Hacking Forensic Investigator
- 312-38 - Certified Network Defender
- 312-50 - CEH Certified Ethical Hacker (312-50v9)
- 312-50v12 - Certified Ethical Hacker v12 Exam
- 312-76v3 - EC-Council Disaster Recovery Professional
- 312-40v2 - Certified Cloud Security Engineer (CCSE) v2
- 612-51 - Certified Responsible AI Governance and Ethics Professional
- 312-49 - Computer Hacking Forensic Investigator
- 312-39 - Certified SOC Analyst
- 212-82 - Certified Cybersecurity Technician
- 312-96 - Certified Application Security Engineer (CASE) - JAVA